Fortify Enterprise ERP Data: Essential AWS RDS Security Strategies
As modern enterprises scale their ERP ecosystems into cloud environments, safeguarding central data repositories becomes mission-critical. Securing your AWS RDS infrastructure requires a defense-in-depth framework designed to protect critical enterprise data from evolving cyber threats and unauthorized access. By combining advanced MySQL 8.1 features, robust network controls, and strict cloud compliance standards, companies can achieve resilient operational continuity.
Why Enterprise Cloud ERP Systems Require Advanced AWS RDS Security
In today's interconnected economy, enterprise resource planning (ERP) platforms manage everything from inventory tracking and logistics to sensitive customer transactions and real-time financial reporting. Migrating these core systems to cloud environments like Amazon Relational Database Service (AWS RDS) provides unprecedented operational scalability. However, centralizing critical business logic inside cloud databases also elevates the risks associated with data breaches, regulatory non-compliance, and unexpected downtime.
Ensuring end-to-end database protection involves more than just setting complex passwords. Cloud-native architectures demand a comprehensive security posture encompassing AWS RDS security best practices, strict identity controls, and continuous system monitoring. According to the IBM Cost of a Data Breach Report 2024, the global average cost of a data breach reached an all-time high of $4.88 million, emphasizing the immense financial risk of unoptimized database infrastructures. As digital supply chains accelerate across retail, manufacturing, and third-party logistics (3PL), business leaders must treat cloud security as a strategic pillar rather than an operational afterthought.
Enforcing Data Protection through Robust Cloud Data Encryption
Data stored within enterprise relational databases represents the intellectual core of your organization. Implementing enterprise-grade cloud data encryption both at rest and in transit ensures that even if bad actors intercept network packets or physically compromise underlying hardware, the data remains unreadable.
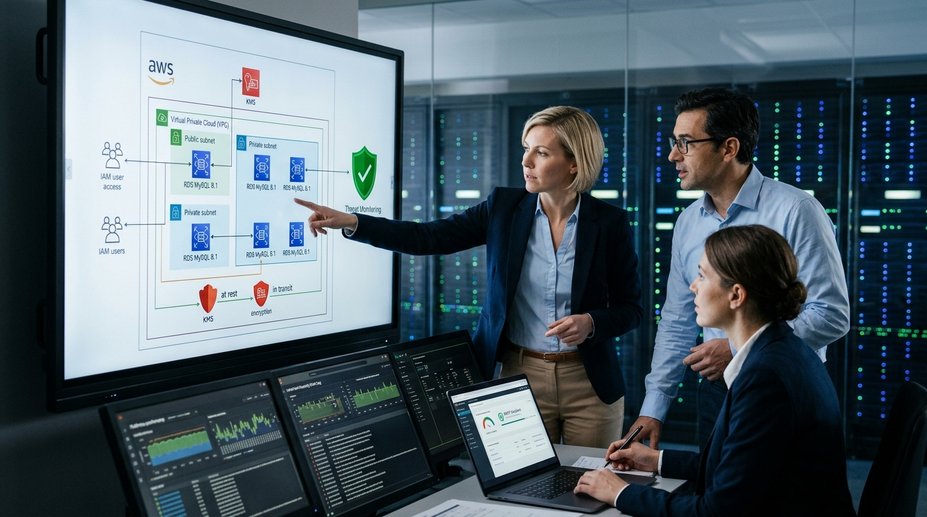
AWS RDS natively integrates with AWS Key Management Service (KMS), enabling automated encryption for database instances, automated backups, read replicas, and system snapshots. Utilizing customer managed keys (CMKs) grants security engineers granular control over encryption key rotation schedules and access permissions. For data in transit, organizations must mandate Transport Layer Security (TLS/SSL) connections across all application-to-database communication channels. Forcing encrypted connections prevents man-in-the-middle attacks, particularly when handling real-time supply chain updates or multi-store inventory syncs across global enterprise channels.
Strengthening Identity and Access Control with IAM Database Authentication
Traditional database management relied heavily on static, hard-coded usernames and passwords stored within application configuration files. This legacy approach exposes enterprises to credentials leakage, privilege escalation, and auditing challenges. Modern cloud compliance standards dictate moving away from permanent credentials toward ephemeral, identity-based access frameworks.
Leveraging IAM database authentication allows enterprise architectures to manage database access directly through AWS Identity and Access Management (IAM). Instead of static passwords, applications request short-lived authentication tokens generated using AWS security credentials. This dynamic access model drastically reduces the attack surface, enforces the principle of least privilege, and integrates seamlessly with centralized identity providers. Furthermore, enterprise IT teams can map granular IAM roles to specific departments—ensuring warehouse staff, logistics managers, and financial analysts only access data necessary for their specific roles.
Disaster Recovery and Automated Backups for Modern Supply Chains
Operational resilience hinges on an enterprise's ability to recover swiftly from infrastructure failures, accidental data loss, or ransomware outbreaks. In high-throughput logistics, manufacturing, and B2B wholesale operations, database downtime directly translates to lost revenue and disrupted fulfillment pipelines. According to recent market analysis from Gartner's 2025 Information Security Forecast, global enterprise spending on risk management and cloud infrastructure protection is projected to surge by 15% as organizations prioritize high-availability operational strategies.
Building a resilient disaster recovery blueprint for AWS RDS involves configuring continuous automated backups alongside manual snapshot schedules. AWS RDS automatically maintains point-in-time recovery (PITR) capabilities, allowing database administrators to restore an environment to any specific second within a configured retention period. Furthermore, establishing multi-region read replicas guarantees high availability and cross-region failover capability. If a primary region experiences an outage, cross-region replication ensures your core enterprise operations remain online with minimal recovery point objectives (RPO) and recovery time objectives (RTO).
Leveraging MySQL 8.1 Features for High-Performance Enterprise Databases
Upgrading your database engine to take full advantage of MySQL 8.1 features brings immediate performance and security benefits to your enterprise architecture. MySQL 8.1 introduces refined privilege management, enhanced query optimization, and dynamic telemetry controls designed to handle heavy enterprise workloads.
Key security enhancements in MySQL 8.1 include dual-password support for zero-downtime password rotations, improved audit logging plugins, and refined access control privileges. Enterprise applications can rotate database service account keys without taking core ERP modules offline, directly eliminating maintenance downtime window constraints. Additionally, optimized query parsing inside MySQL 8.1 ensures fast database response times for complex inventory queries, financial ledger computations, and order processing tasks.
Securing Network Boundaries: VPC Isolation and Bastion Hosts
Proper network isolation serves as the first line of defense in database protection. Under no circumstances should an enterprise AWS RDS instance be assigned a public IP address or placed within a public network subnet. Exposing databases directly to the open internet invites continuous automated brute-force attacks and vulnerability scanning.
Establishing strict VPC isolation requires deploying database instances exclusively inside private Virtual Private Cloud (VPC) subnets. Network Access Control Lists (NACLs) and security groups should be configured using strict ingress rules, permitting inbound traffic exclusively on the database port (e.g., port 3306 for MySQL) from designated application servers or secure Bastion hosts. When system administrators or database engineers require direct maintenance access, connections must be funneled through secure VPN gateways or AWS Systems Manager Session Manager, bypassing the need for public IP exposure completely.
Continuous Threat Monitoring and Cloud Compliance
Maintaining security demands ongoing monitoring and continuous audit logging. Real-time threat monitoring provides security operations center (SOC) teams with immediate visibility into anomalous login attempts, unauthorized schema changes, or unusual data exfiltration patterns.
Integrating Amazon GuardDuty for RDS allows enterprises to utilize machine learning models that monitor database login behavior and detect suspicious activity automatically. Combining GuardDuty with AWS CloudTrail records all API calls made to the database infrastructure, creating an immutable audit trail required for cloud compliance frameworks such as SOC 2, ISO 27001, and GDPR. Enhanced Monitoring in AWS RDS provides real-time metrics on CPU utilization, memory consumption, and I/O performance, enabling proactive resource optimization before latency affects enterprise operational workflows.
Seven Core Strategies for AWS RDS Database Protection
To establish a resilient cloud environment capable of protecting sensitive operational data, implement these seven actionable infrastructure strategies:
- 1. Data Protection & Robust Encryption: Enforce AES-256 encryption at rest using AWS KMS and mandate TLS/SSL protocols for all data in transit across your MySQL 8.1 databases.
- 2. Automated Backups & Disaster Recovery: Establish continuous automated snapshot schedules and configure multi-region read replicas to guarantee minimal data loss and rapid recovery in emergency scenarios.
- 3. Advanced Access Control & IAM: Replace static credentials with short-lived AWS IAM database authentication tokens while strictly applying the principle of least privilege.
- 4. Leveraging MySQL 8.1 Innovations: Capitalize on MySQL 8.1 enhancements, including fine-grained privilege management, improved audit logging capabilities, and optimized query execution.
- 5. Strict Network Isolation: Deploy RDS instances exclusively inside private VPC subnets, disabling public accessibility and routing database traffic through secure Bastion hosts or VPNs.
- 6. Real-Time Auditing & Monitoring: Integrate Amazon GuardDuty, AWS CloudTrail, and RDS Enhanced Monitoring to continuously track database performance and detect anomalous access patterns instantly.
- 7. Automated Patching & Maintenance: Schedule regular maintenance windows to seamlessly apply security patches, engine updates, and critical system fixes.
Bridging Security, Logistics, and ERP Operations
As enterprise operations expand across e-commerce platforms, distribution networks, and multi-location warehouses, the integrity of your core database directly impacts customer satisfaction and operational agility. Securing your database layer guarantees that real-time stock updates, automated invoicing workflows, and procurement routines operate without interruption.
Building a secure cloud infrastructure provides the necessary peace of mind to focus on scaling core business activities. By systematically addressing network isolation, identity management, database protection, and automated disaster recovery, business leaders can confidently deploy modern ERP capabilities that support long-term revenue growth and sustainable market leadership.
Empower your enterprise with seamless operational control, robust security standards, and automated supply chain intelligence by discovering how Logzi ERP transforms modern business management today.